
Celiveo 365 relies on the Oauth2 protocol to provide state-of-the-art access-control.
It requires a simple one-time configuration in Azure and in the Celiveo 365 Web Admin portal.
You first need to create and register an Azure Authentication application that will be used by Celiveo 365 Scan to authenticate against Entra ID identity platform and to communicate with OneDrive and Exchange Online.
Subscription Requirements
- Microsoft Entra ID Account is required to access the customer tenant and Register the Application.
- The used Microsoft Entra ID Account requires the following roles:
- Privileged Role Administrator Role
- App development admin
- Cloud application administrator
Application Registration
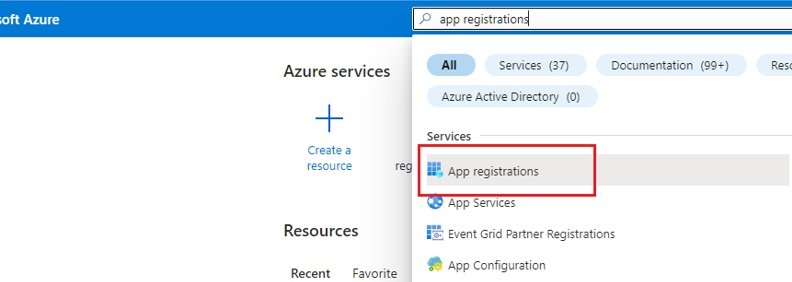
- Sign in to the Azure portal and search “App registrations”
![]()
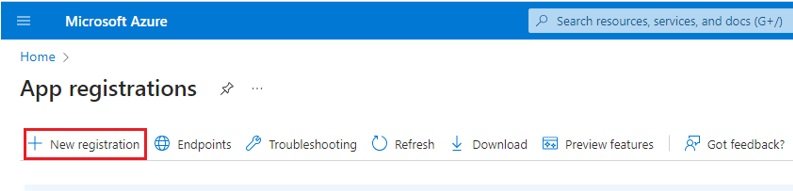
- Click “New registration” in “App registrations” as shown below

- Enter a name “Celiveo 365 Scan – OneDrive” for application and select “Accounts in this organizational directory only (Customer Tenant only- Single tenant)” and Save.
![]()
- Under Manage > Authentication, select the supported Account Type “Accounts in this organizational director,’ only (Customer Tenant only – Single tenant)”. in Advanced settings set Enable the following mobile and desktop flow to Yes and Save.
![]()
- Under Manage > API permissions, press “Add a permission”.
![]()
- Under Microsoft APIs select “Microsoft Graph”.
![]()
- Select “Delegated permissions”, under the Select permissions search type “Files.ReadWrite” or select it under Files > * Files.ReadWrite* and press Add Permissions. Note: This only allows the app to read. create. update and delete the signed-in user’s files.
![]()
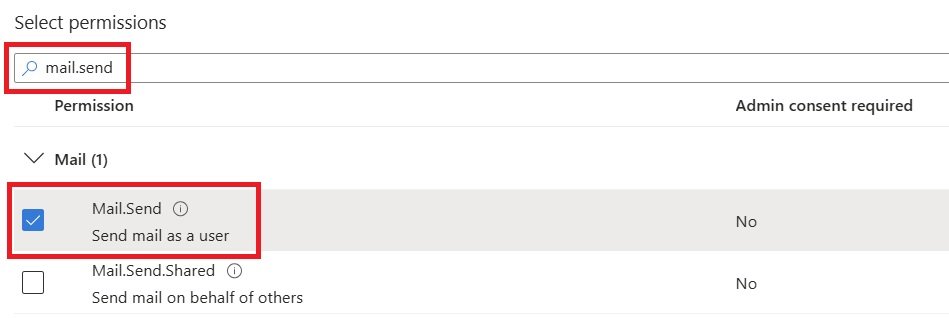
Do the same with Mail.Send to authorize the direct scan to Microsoft 365 Exchange Online (secure email sending using the user identify with Oauth2 protocol)
![Configuring Direct scan to Microsoft 365 email from printers with Celiveo 365 - Azure configuration]()
- Under Overview copy the Application (Client) ID and Directory (tenant) ID data for application configuration in Web Admin. Process described here.
![]()



Last modified:
11 August 2026
Post your comment on this topic.